Spring Security Kerberos 示例
本部分参考文档介绍了示例项目。示例可以通过从 github.com/spring-projects/spring-security-kerberos 构建主发行版来手动编译。
如果按原样运行示例,在应用正确的配置之前它将无法正常工作。有关各示例的具体说明,请参阅下面的注释。
Security Server Windows Auth Sample 用于 Windows 环境的示例
Security Server Side Auth Sample 使用服务端认证器的示例
Security Server Spnego and Form Auth Sample 使用 spnego 和表单进行票据验证的示例
Security Client KerberosRestTemplate Sample 用于 KerberosRestTemplate 的示例
Security Server Windows Auth 示例
此示例的目标:
- 在 Windows 环境中,用户将能够使用登录 Windows 时输入的 Windows Active Directory 凭据登录应用程序。不应再有任何询问用户 ID/密码凭据的提示。
- 在非 Windows 环境中,用户将看到一个输入 Active Directory 凭据的界面。
server:
    port: 8080
    app:
        ad-domain: EXAMPLE.ORG
        ad-server: ldap://WIN-EKBO0EQ7TS7.example.org/
        service-principal: HTTP/neo.example.org@EXAMPLE.ORG
        keytab-location: /tmp/tomcat.keytab
        ldap-search-base: dc=example,dc=org
        ldap-search-filter: "(| (userPrincipalName={0}) (sAMAccountName={0}))"
在上面你可以看到此示例的默认配置。你可以使用常规的 Spring Boot 技巧来覆盖这些设置,例如使用命令行选项或自定义 application.yml 文件。
运行服务器。
$ java -jar sec-server-win-auth-2.2.0.jar
在 Linux 上,你可能需要使用自定义的 Kerberos 配置,可以通过 -Djava.security.krb5.conf=/path/to/krb5.ini 或 GlobalSunJaasKerberosConfig bean 来实现。
有关如何使用 Windows Kerberos 环境的更多说明,请参阅 设置 Windows 域控制器。
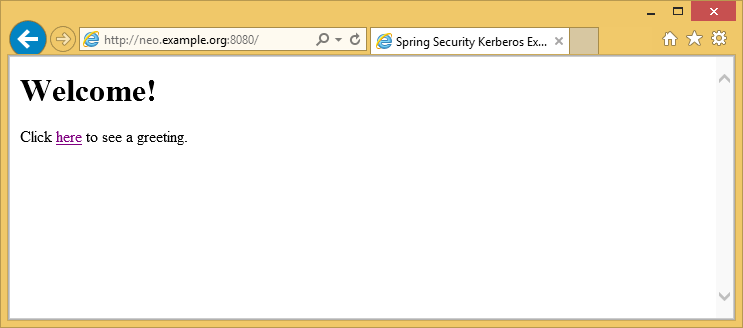
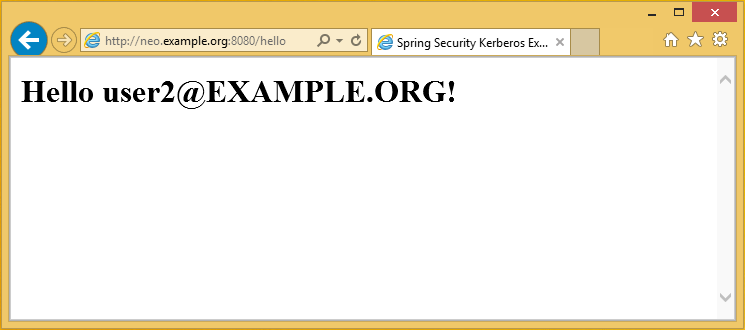
使用域凭据登录 Windows 8.1 并访问示例
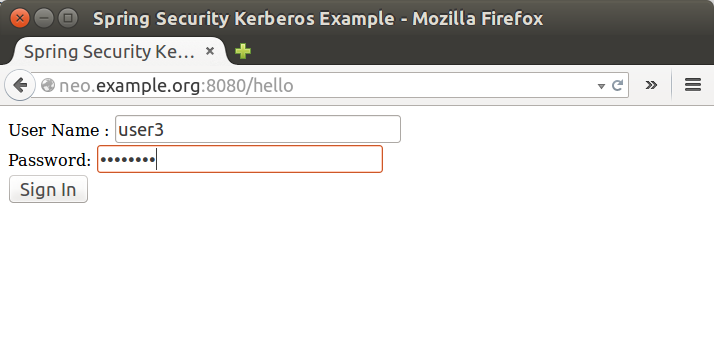
从非 Windows 虚拟机访问示例应用程序,并手动使用域凭据。
Security Server Side Auth 示例
此示例演示了服务器如何通过表单登录传入的用户凭据,在 Kerberos 环境中对用户进行身份验证。
运行服务器。
$ java -jar sec-server-client-auth-2.2.0.jar
server:
    port: 8080
Security Server Spnego 和表单认证示例
此示例演示了如何配置服务器以接受来自浏览器的基于 Spnego 的协商,同时仍能回退到基于表单的身份验证。
使用 user1 主体设置 MIT Kerberos,使用凭据手动进行 Kerberos 登录。
$ kinit user1
Password for user1@EXAMPLE.ORG:

$ klist
Ticket cache: FILE:/tmp/krb5cc_1000
Default principal: user1@EXAMPLE.ORG

Valid starting     Expires            Service principal
10/03/15 17:18:45  11/03/15 03:18:45  krbtgt/EXAMPLE.ORG@EXAMPLE.ORG
  renew until 11/03/15 17:18:40
或者使用 keytab 文件。
$ kinit -kt user2.keytab user1

$ klist
Ticket cache: FILE:/tmp/krb5cc_1000
Default principal: user2@EXAMPLE.ORG

Valid starting     Expires            Service principal
10/03/15 17:25:03  11/03/15 03:25:03  krbtgt/EXAMPLE.ORG@EXAMPLE.ORG
  renew until 11/03/15 17:25:03
运行服务器。
$ java -jar sec-server-spnego-form-auth-2.2.0.jar
现在你应该能够打开浏览器,让它使用现有票据进行 Spnego 身份验证。
有关配置浏览器使用 Spnego 的更多说明,请参阅 配置浏览器以进行 Spnego 协商。
server:
    port: 8080
app:
    service-principal: HTTP/neo.example.org@EXAMPLE.ORG
    keytab-location: /tmp/tomcat.keytab
Security Client KerberosRestTemplate 示例
这是一个使用 Spring RestTemplate 访问受 Kerberos 保护的资源的示例。你可以将此示例与 Security Server Spnego 和表单认证示例 一起使用。
默认应用程序的配置如下所示。
app:
    user-principal: user2@EXAMPLE.ORG
    keytab-location: /tmp/user2.keytab
    access-url: http://neo.example.org:8080/hello
使用 user1 主体设置 MIT Kerberos,使用凭据手动进行 Kerberos 登录。
$ java -jar sec-client-rest-template-2.2.0.jar --app.user-principal --app.keytab-location
在上面我们简单地将 app.user-principal 和 app.keytab-location 设置为空值,这会禁用 keytab 文件的使用。
如果操作成功,你应该会看到下面带有 user1@EXAMPLE.ORG 的输出。
<html xmlns="http://www.w3.org/1999/xhtml"
      xmlns:sec="http://www.thymeleaf.org/thymeleaf-extras-springsecurity3">
  <head>
    <title>Spring Security Kerberos Example</title>
  </head>
  <body>
    <h1>Hello user1@EXAMPLE.ORG!</h1>
  </body>
</html>
或者使用带有 keytab 文件的 user2。
$ java -jar sec-client-rest-template-2.2.0.jar
如果操作成功,你应该会看到下面带有 user2@EXAMPLE.ORG 的输出。
<html xmlns="http://www.w3.org/1999/xhtml"
      xmlns:sec="http://www.thymeleaf.org/thymeleaf-extras-springsecurity3">
  <head>
    <title>Spring Security Kerberos Example</title>
  </head>
  <body>
    <h1>Hello user2@EXAMPLE.ORG!</h1>
  </body>
</html>